PerspectiveGraph
An open-source attack-path engine
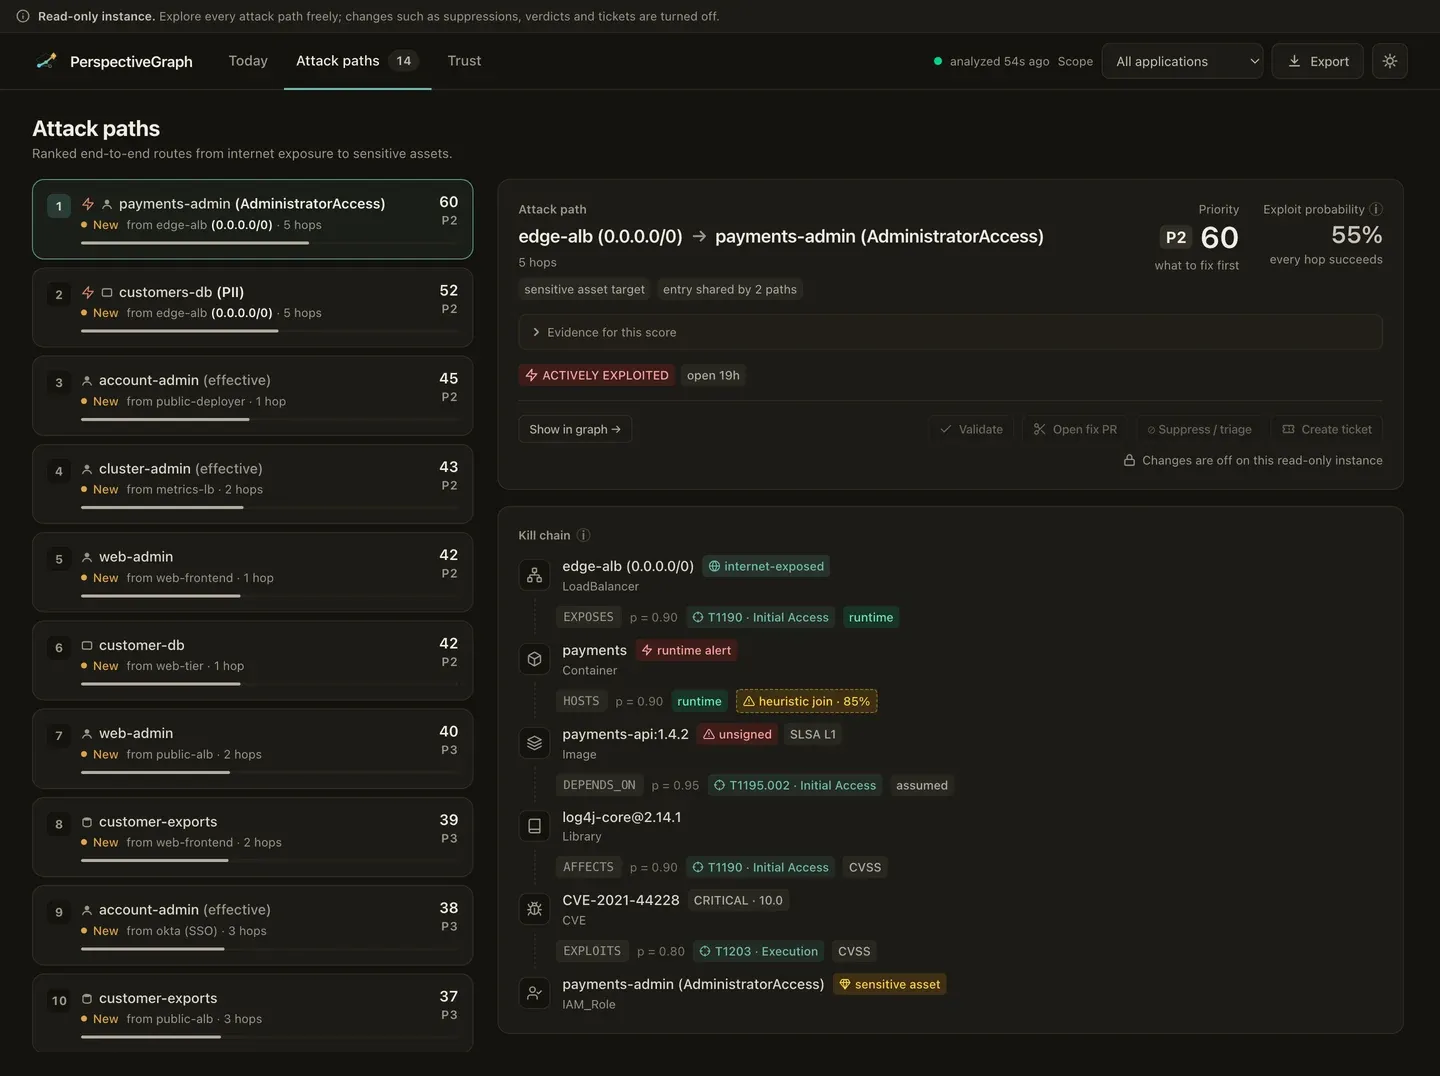
An open-source engine that asks one question of every pull request: does this change open a path from the internet, through too much privilege, to something worth stealing? Each hop gets a probability instead of a severity label, and where the engine isn't sure, it says so rather than rounding up. I also built a red-team oracle that checks its conclusions against the live AWS policy-evaluation API - and it caught my own engine ignoring an IAM permissions boundary, and reporting an escalation the boundary made impossible. That false positive is a regression test now.
Highlights
- Apache 2.0, public repository, CI running on every commit
- Container images signed with cosign, with SBOM and SLSA build provenance
- Graded in CI against four CloudGoat-shaped scenarios, including two that must produce no finding
- Privilege hops validated against the live AWS policy-evaluation API